TheConitivplatform
Scoring, questionnaires, audits, cyber rating, third-party management — all in a single interface. For all your departments. Managing third-party risk with spreadsheets, emails and five different tools is no longer sustainable.
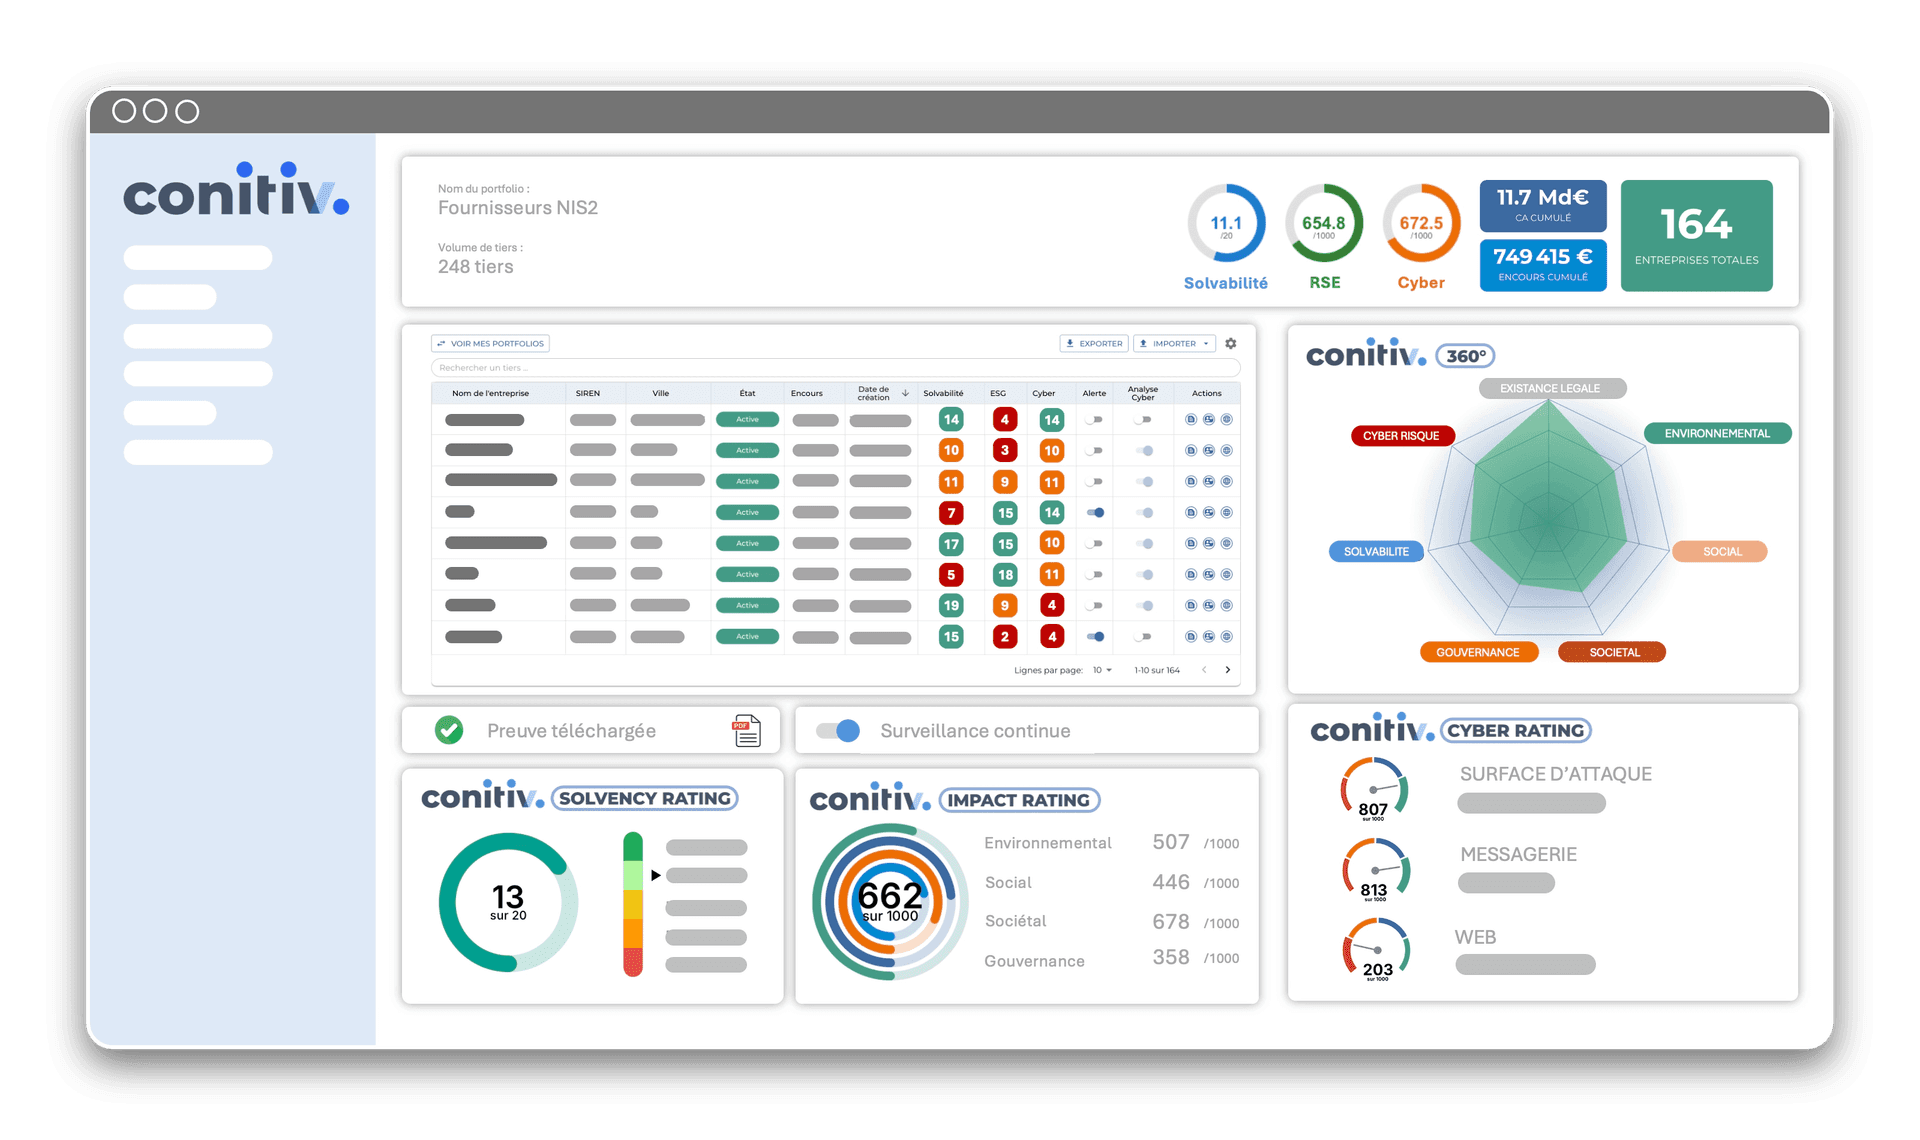
Managing third-party risk with fragmented tools is no longer sustainable
Conitiv brings everything together in a single platform. Each department accesses the data relevant to them, from one unified environment.
Fragmented tools
Excel, emails, supplier portals, scoring tools, compliance databases… Five different tools for a single process.
Too many departments involved
Compliance, procurement, IT, finance, CSR, DPO, risk… Each department has its own needs and its own files.
Regulatory explosion
NIS2, DORA, GDPR, CSRD, CSDDD, ISO 27001… Requirements are multiplying and evidence must be centralized.
Scattered evidence
When you need to produce a compliance file during an audit, documents are scattered across emails, SharePoint and local folders.
The 5 modules of the platform
From automated scoring to evidence-based audits, complete third-party risk coverage in a single interface.
Automated 360° Data & Scoring
The platform leverages hundreds of millions of data points to assign each third party a multi-dimensional score: solvency (score out of 20, 50+ financial ratios, 12M companies), CSR (Conitiv Impact Rating out of 1,000, 80 ESG criteria, 7M companies), cyber (score out of 1,000, 1M companies) and legal existence. Non-intrusive, non-declarative, continuously updated.
Third-party portfolio
Import your suppliers (Excel, CSV, JSON), enrich them automatically, segment by criticality (A, B, C) and visualize risk levels in a consolidated dashboard. Filterable by score, sector, regulation. Your third-party risk management cockpit.
Compliance questionnaires
Deploy questionnaires aligned with each framework (GDPR, NIS2, DORA, ISO 27001, TISAX, CSRD…) directly from the platform. Your third parties respond online, attach their evidence. Responses are historized and integrated into the overall scoring.
Evidence-based audits
For strategic third parties, declarations are not enough. Our partners — PASSI-qualified — verify declared measures on evidence: security policies, procedures, certifications, technical reports. The audit report is centralized and legally enforceable.
Advanced cyber rating
Advanced analysis of your third parties’ digital exposure: attack surface, open ports, DNS and email configuration, detectable vulnerabilities. Score broken down by perimeter. Continuous monitoring for 12 months with alerts on degradation.
One platform, all your departments
Third-party risk is cross-functional. The Conitiv platform is too. Each department accesses the data and features that match its responsibilities.
Compliance department
Regulatory questionnaires, evidence-based audits, corrective action plans, compliance indicators.
DPO
GDPR assessment of subcontractors, evidence centralization, cyber scoring of data-handling providers.
Risk department
Third-party mapping, consolidated scoring, weak signal detection, dynamic monitoring.
Procurement department
Solvency and CSR scoring in the supplier selection process, renewal tracking.
CIO / CISO
Third-party cyber rating, vulnerability tracking, integration into IT risk management.
Finance department
Solvency scoring, recommended credit limits, failure anticipation.
The platform integrates into the TPRM Advanced program for comprehensive support. Also discover access via API and how to evaluate your suppliers.
The platform in numbers
Companies covered in solvency scoring
Companies rated on the Conitiv Impact Rating (CSR)
Companies assessed on cyber risk
Financial ratios calculated automatically
ESG criteria analyzed by CSR scoring
Modules integrated in a single platform
Frequently asked questions
Ready to centralize your third-party risk management?
Discover the Conitiv platform and its 5 integrated modules to manage your third-party ecosystem from a single interface.
expert Conitiv